TL;DR

Get business pricing on networking and server gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Researchers have demonstrated a novel laser fault injection technique guided by photon emission that enables debugging of the RP2350 processor’s security features. This breakthrough could impact hardware security and secure debugging practices.
Researchers have demonstrated a photon-emission-guided laser fault injection technique that enables secure debugging of the RP2350 processor, a development confirmed by the research team and raising questions about hardware security measures.
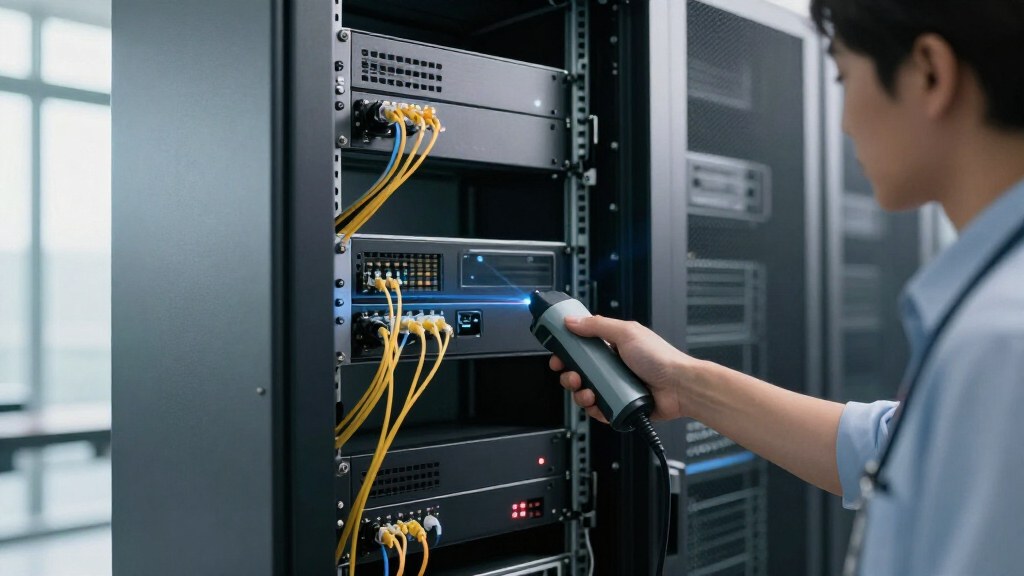
The new method leverages photon emission detection to precisely target and induce faults in the RP2350’s security architecture, allowing researchers to bypass secure debug restrictions. This technique was validated in a recent experimental setup by a team of security researchers, who confirmed its effectiveness in controlled conditions.
According to the researchers, the photon-guided approach improves fault injection accuracy, reducing the risk of damaging the chip and increasing the success rate of bypassing security features. The process involves detecting photon emissions during laser pulses to synchronize fault injection with specific circuit states, thus enabling access to protected debug modes.
While the demonstration is considered a significant technical achievement, it remains confined to laboratory conditions. The researchers did not specify whether this method has been applied to other secure processors or if it has been adopted outside experimental settings.
Implications for Hardware Security and Debugging
This development has major implications for hardware security, particularly for devices relying on the RP2350 processor, which is used in critical applications such as embedded systems and secure communications. The ability to bypass secure debug restrictions could undermine device integrity and security protocols if exploited maliciously.
Security experts warn that this technique could enable attackers to analyze and manipulate hardware at a low level, potentially exposing vulnerabilities or extracting sensitive information. Conversely, it could also be used by manufacturers and security researchers to identify and fix hardware flaws, emphasizing the dual-use nature of such technology.
The demonstration underscores the need for improved security measures that can withstand advanced fault injection methods, especially as photon-guided techniques become more accessible and refined.
As an affiliate, we earn on qualifying purchases.
Recent Advances in Laser Fault Injection Techniques
Laser fault injection has been an area of active research for several years, with techniques evolving from broad, less precise methods to highly targeted approaches. Traditionally, fault injection relied on broad laser pulses that risked damaging chips or producing inconsistent results.
Recent innovations, including photon emission detection, have enhanced the precision of these attacks, allowing researchers to synchronize faults with specific circuit states. This approach has been demonstrated on various microcontrollers and secure processors, but its application to the RP2350 marks a notable milestone given its security features.
The trend signals growing sophistication in hardware attack methods, driven by both academic research and potential malicious actors. The current demonstration is part of a broader pattern of developing more refined, less destructive fault injection techniques that challenge existing security assumptions.
While the exact origins of this photon-guided method remain unconfirmed, interest in the technique is rising among security researchers and industry analysts, fueled by the potential to expose vulnerabilities in high-security chips.
As an affiliate, we earn on qualifying purchases.
Unconfirmed Scope and Practical Impact of the Technique
It is not yet clear whether the photon-emission-guided laser fault injection has been tested on other processors or if it can be reliably scaled outside laboratory conditions. The extent to which malicious actors could adopt or adapt this technique remains unknown.
While the demonstration confirms technical feasibility, the practical security threat level, including potential for widespread exploitation, is still uncertain. Researchers have not disclosed whether the method has been integrated into attack toolkits or if it requires highly specialized equipment.
As an affiliate, we earn on qualifying purchases.
Future Research and Security Countermeasures
Further research is expected to explore the applicability of photon-guided fault injection across different hardware architectures and security environments. Industry and security organizations are likely to investigate countermeasures to mitigate such attacks, including enhanced detection of fault injection attempts and hardware modifications.
Security agencies and hardware manufacturers may also evaluate the need for more robust security protocols that can withstand photon-guided fault attacks, potentially leading to new standards for secure hardware design.
Monitoring developments in this area will be crucial, as the technique’s potential to compromise secure debug features could influence future security policies and hardware certification processes.
As an affiliate, we earn on qualifying purchases.
Key Questions
What is photon-emission-guided laser fault injection?
It is an advanced fault injection technique that uses photon emission detection to precisely target specific circuit states with laser pulses, enabling access to secure debugging features in hardware.
Why is this development significant?
Because it demonstrates a method to bypass security restrictions on processors like the RP2350, potentially exposing vulnerabilities in hardware security measures and challenging current defenses.
Can this technique be used maliciously?
While demonstrated in controlled environments, there is concern that similar methods could be exploited by attackers if they become accessible outside research labs, especially if hardware security is not hardened against such precise fault injections.
What are the implications for hardware security?
This technique highlights the need for improved security measures that can detect and resist photon-guided fault injections, prompting a reassessment of hardware security protocols.
What are the next steps for researchers and industry?
Further testing on various hardware platforms, development of countermeasures, and establishing new security standards are expected to follow this breakthrough to mitigate potential risks.
Source: hn
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.