Cloud-based firewall appliances combine on-site network protection with management through a cloud platform, but the right fit depends on whether you value centralized control, security services, wireless, or room to grow. I rank the Meraki MX75-HW as the best overall for organizations that want cloud-first management and integrated SD-WAN. The Sophos XGS 118 is a strong alternative for buyers choosing among protection-service bundles, while the Fortinet FortiGate-60F suits teams looking for a security-focused appliance with FortiGuard services. The main tradeoffs are cloud-management convenience versus control and licensing complexity, plus the cost of capacity headroom you may not need. Read on for how the 15 options differ and which buyer each one suits.

Get business pricing on networking and server gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Key Takeaways
- Meraki MX75-HW leads for cloud-first management: It pairs centralized cloud administration with SD-WAN, making it the clearest all-around pick for teams that value ease of oversight.
- Sophos XGS 118 bundles change the buying decision: The 1-year Xstream, 3-year Xstream, Standard Protection, and hardware-only versions share a platform but differ in included protection and commitment.
- Wireless is a meaningful dividing line: SonicWall TZ570W and TZ280W add wireless to their firewall role, while wired models may suit sites that already have separate access points.
- Hardware size and service coverage are separate choices: Options such as the MX105 and MX95 bundles target different capacity needs, while several Sophos and SonicWall listings vary mainly by security services.
- Not every option fits a managed business network: Firewalla Purple SE is aimed at home and small-business use, while higher-tier appliances such as the TZ670 are better suited to more demanding network requirements.
| Meraki MX75-HW Cloud-Managed Security and SD-WAN Appliance | 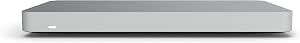 | Best for Simple Cloud-Managed Branches | Model: MX75-HW | Firewall throughput: Up to 1 Gbps | VPN throughput: Up to 500 Mbps | VIEW LATEST PRICE | See Our Full Breakdown |
| Sophos XGS 118 Gen2 Network Security Appliance with 1-Year Xstream Protection |  | Best for High-Throughput Security with Included Protection | Model: XGS 118 Gen2 | Firewall throughput: 15.5 Gbps | Ports: 9 x 2.5 GE copper and 1 x SFP fiber | VIEW LATEST PRICE | See Our Full Breakdown |
| Sophos XGS 118 Gen2 Network Security Appliance with 3-Year Xstream Protection | | Best Multi-Year Xstream Bundle | Model: XGS 118 Gen2 | Firewall throughput: Up to 15.5 Gbps | Ports: 9 x 2.5 GE copper and 1 x SFP fiber | VIEW LATEST PRICE | See Our Full Breakdown |
| Sophos XGS 118 Gen 2 Network Security Appliance with 1-Year Standard Protection | | Best for Core Business Firewall Features | Model: XGS 118 Gen 2 | Firewall throughput: Up to 15.5 Gbps | Ports: 9 x 2.5 GE copper and 1 x SFP fiber | VIEW LATEST PRICE | See Our Full Breakdown |
| SonicWall TZ570 Gen7 Firewall Appliance |  | Best for Segmentation and Branch Control | Model: TZ570 | Firewall throughput: Up to 4 Gbps | Concurrent connections: Up to 1.25 million | VIEW LATEST PRICE | See Our Full Breakdown |
| SonicWall TZ570W Wireless Gen7 Firewall |  | Best for Built-In Business Wi-Fi | Model: TZ570W | Wireless: Dual-band 802.11ac Wave 2 (Wi-Fi 5) | Throughput: 3.0 Gbps | VIEW LATEST PRICE | See Our Full Breakdown |
| Sophos XGS 118 Gen2 Network Security Appliance (Hardware Only) | | Best for Multi-Gig Wired Networks | Model: XGS 118 Gen2 | Copper ports: 9 x 2.5 GE | Fiber port: 1 x SFP | VIEW LATEST PRICE | See Our Full Breakdown |
| Fortinet FortiGate-60F Network Security Appliance with 1-Year FortiGuard UTP and FortiCare Premium |  | Best Subscription-Ready Bundle | Model: 60F-1YR-UTP | Operating system: FortiOS | Ports: 13 | VIEW LATEST PRICE | See Our Full Breakdown |
| SonicWall TZ280W Next-Generation Firewall Appliance |  | Best for Wi-Fi 6 Branch Offices | Model: TZ280W | Firewall inspection throughput: Up to 2.5 Gbps | Threat prevention throughput: Up to 1 Gbps | VIEW LATEST PRICE | See Our Full Breakdown |
| MX105-HW Cloud-Managed Security Appliance |  | Best for Cloud-Managed Rack Deployments | Throughput: Up to 3 Gbps | Ethernet ports: 10 Gigabit Ethernet ports | Management: Cloud-managed | VIEW LATEST PRICE | See Our Full Breakdown |
| SonicWall TZ270 Gen 7 Firewall with 3-Year APSS and 1-Year Cloud Secure Edge |  | Best Bundled Protection for Small Branches | Model: TZ270 Gen 7 | Operating system: SonicOS 7 | Security subscription: 3-year Advanced Protection Service Suite (APSS) | VIEW LATEST PRICE | See Our Full Breakdown |
| SonicWall TZ80 High Availability Firewall Appliance |  | Best for High-Availability Failover | Model: TZ80 | Part number: 03-SSC-2749 | Operating system: SonicOS 8 | VIEW LATEST PRICE | See Our Full Breakdown |
| SonicWall TZ670 Gen7 Firewall – Multi‑Gig Throughput Wi‑Fi Security Appliance |  | Best for High-Throughput Distributed Networks | Firewall throughput: 5 Gbps | Threat-prevention throughput: 2.5 Gbps | Concurrent connections: 1.5 million | VIEW LATEST PRICE | See Our Full Breakdown |
| Firewalla Purple SE Cyber Security Firewall for Home & Business – Malware Protection, Parental Controls, VPN Server, No Monthly Fee |  | Best for App-Controlled Home and Small Networks | Model: Purple SE | IPS throughput: 500 Mbps | LAN port speed: 100 Mbps | VIEW LATEST PRICE | See Our Full Breakdown |
| Meraki MX95-HW Security Appliance Bundle |  | Best for Cloud-Managed Branch Operations | Model: MX95-HW | Throughput: 2 Gbps | User capacity: Up to 500 users | VIEW LATEST PRICE | See Our Full Breakdown |
| cloud based firewall appliance | Model | Operating system | Firewall throughput |
|---|---|---|---|
| Meraki MX75-HW Cloud-Managed S | MX75-HW | — | Up to 1 Gbps |
| Sophos XGS 118 Gen2 Network Se | XGS 118 Gen2 | Sophos Firewall OS | 15.5 Gbps |
| Sophos XGS 118 Gen2 Network Se | XGS 118 Gen2 | — | Up to 15.5 Gbps |
| Sophos XGS 118 Gen 2 Network S | XGS 118 Gen 2 | Sophos OS | Up to 15.5 Gbps |
| SonicWall TZ570 Gen7 Firewall | TZ570 | SonicOS 7.0 | Up to 4 Gbps |
| SonicWall TZ570W Wireless Gen7 | TZ570W | SonicOS 7.0 | — |
| Sophos XGS 118 Gen2 Network Se | XGS 118 Gen2 | Sophos Firewall OS | Up to 15.5 Gbps |
| Fortinet FortiGate-60F Network | 60F-1YR-UTP | FortiOS | — |
| SonicWall TZ280W Next-Generati | TZ280W | — | — |
| MX105-HW Cloud-Managed Securit | — | Cisco IOS | — |
| SonicWall TZ270 Gen 7 Firewall | TZ270 Gen 7 | SonicOS 7 | — |
| SonicWall TZ80 High Availabili | TZ80 | SonicOS 8 | Up to 750 Mbps |
| SonicWall TZ670 Gen7 Firewall | — | — | 5 Gbps |
| Firewalla Purple SE Cyber Secu | Purple SE | Linux | — |
| Meraki MX95-HW Security Applia | MX95-HW | Meraki OS | — |
More Details on Our Top Picks
Meraki MX75-HW Cloud-Managed Security and SD-WAN Appliance
I’d choose the Meraki MX75-HW for a small branch where centralized setup and ongoing cloud management matter more than maximum throughput. Zero-touch provisioning, automatic failover, SD-WAN, VPN, and integrated intrusion prevention and malware protection bring several branch-network jobs into one appliance. Its stated capacity of up to 200 users and 1 Gbps firewall throughput make its scale clearer than the more powerful Sophos XGS 118 Gen2, which offers 15.5 Gbps and faster 2.5 GbE ports. The Meraki’s tradeoff is its licensing: a license is not included, so the hardware alone does not provide the full cloud-managed security service described here. I’d also look beyond it for a larger site or one needing multi-gigabit LAN ports.
Pros:- Cloud management and zero-touch provisioning support simpler branch deployment.
- Combines SD-WAN, site-to-site and client VPN, and automatic failover.
- Includes intrusion prevention, malware protection, and content filtering.
- Layer 7 traffic shaping can help prioritize selected application traffic.
Cons:- A license is not included, adding a separate requirement for the cloud-managed service.
- The listed capacity is limited to deployments of up to 200 users.
- Its 1 Gbps LAN port bandwidth is less suited to networks that need multi-gigabit wired links.
Best for: Small branch offices with up to 200 users that want cloud-managed security, SD-WAN, VPN, and automatic failover in one appliance.
Not ideal for: Organizations that need multi-gigabit LAN connectivity, higher stated firewall throughput, or a complete licensed service in the appliance listing.
- Model:MX75-HW
- Firewall throughput:Up to 1 Gbps
- VPN throughput:Up to 500 Mbps
- Supported users:Up to 200
- WAN ports:3: 1 SFP and 2 GbE
- LAN port bandwidth:1 Gbps
- License:Not included
- Warranty:Limited lifetime warranty
Our verdict“Choose the MX75-HW for a modest branch that values straightforward Meraki cloud management, provided you account for the separate license.”
Sophos XGS 118 Gen2 Network Security Appliance with 1-Year Xstream Protection
The Sophos XGS 118 Gen2 with one-year Xstream Protection suits businesses that want substantial stated firewall throughput and a broad security subscription from the outset. The package lists 15.5 Gbps firewall throughput, nine 2.5 GE copper ports, and an SFP fiber port, giving a wired office more connection options than the Meraki MX75-HW’s 1 Gbps LAN bandwidth. Xstream Protection adds cloud sandboxing, zero-day defense, email filtering, intrusion prevention, and automated threat response; Sophos Central provides cloud-based management. The tradeoff is that the included protection term is one year, so buyers should plan for service beyond that period. It is also a wired security appliance, not a wireless access point. Compared with the Standard Protection XGS 118, this configuration emphasizes the broader Xstream security package.
Pros:- Lists up to 15.5 Gbps firewall throughput.
- Nine 2.5 GE copper ports and one SFP fiber port support flexible wired connections.
- One-year Xstream Protection includes sandboxing, zero-day defense, email filtering, and intrusion prevention.
- Sophos Central cloud management works alongside VPN and SD-WAN support.
Cons:- The included Xstream Protection term is specified for one year.
- No wireless networking is listed.
- Its business security feature set may require more setup and administration than a basic branch firewall.
Best for: Small and midsize businesses with fast wired networks that want cloud-managed firewall security and a broad protection bundle for the first year.
Not ideal for: Teams looking for built-in wireless networking or a subscription arrangement that does not require planning beyond one year.
- Model:XGS 118 Gen2
- Firewall throughput:15.5 Gbps
- Ports:9 x 2.5 GE copper and 1 x SFP fiber
- Total ports:10
- LAN port bandwidth:2500 Mbps
- Subscription:1-year Xstream Protection
- Management:Sophos Central cloud management
- Operating system:Sophos Firewall OS
Our verdict“Pick this XGS 118 configuration for high-throughput wired security with Xstream Protection included for the first year.”
Sophos XGS 118 Gen2 Network Security Appliance with 3-Year Xstream Protection
This XGS 118 package stands out for buyers who want three years of Xstream Protection paired with Sophos Central cloud management. Like the one-year Xstream version, it lists 15.5 Gbps firewall throughput, nine 2.5 GE copper ports, and an SFP fiber port, plus security features such as cloud sandboxing, TLS inspection, and intrusion prevention. Its main distinction is the longer stated protection term, which makes it a better fit for organizations that prefer to set a multi-year service horizon rather than revisit coverage after the first year. Compared with the one-year Xstream configuration, the hardware and core port layout are similar; the term is the key differentiator. The listing also mentions Wi-Fi 6 without clarifying whether wireless hardware is built in, so I would not select it as a wireless solution without confirming that detail.
Pros:- Includes a stated three years of Xstream Protection.
- Lists up to 15.5 Gbps firewall throughput with nine 2.5 GE copper ports and one SFP port.
- Xstream features include cloud sandboxing, TLS inspection, and intrusion prevention.
- Sophos Central, VPN, and SD-WAN support centralized management and connectivity.
Cons:- The listing does not clarify whether the stated Wi-Fi 6 specification means wireless hardware is built in.
- A business-oriented feature set may be more complex than a home or basic small-office firewall needs.
- The longer protection term may not suit buyers who want to choose coverage one year at a time.
Best for: Business IT teams seeking a Sophos XGS 118 with a stated three-year Xstream Protection term and cloud-managed security.
Not ideal for: Buyers who need confirmed built-in Wi-Fi, prefer a basic home firewall, or do not want a multi-year protection bundle.
- Model:XGS 118 Gen2
- Firewall throughput:Up to 15.5 Gbps
- Ports:9 x 2.5 GE copper and 1 x SFP fiber
- Total ports:10
- LAN port bandwidth:2500 Mbps
- Subscription:3 years of Xstream Protection
- Warranty duration:3 years
- Wi-Fi specification:Wi-Fi 6 listed; built-in wireless hardware is not clarified
Our verdict“Choose this version over the one-year Xstream XGS 118 when a stated three-year protection term is the priority and wireless capability is not assumed.”
Sophos XGS 118 Gen 2 Network Security Appliance with 1-Year Standard Protection
I’d place this Sophos XGS 118 configuration below the Xstream bundles for buyers who want a defined set of core business firewall capabilities rather than the broader protection package. It lists firewall, VPN, intrusion prevention, web security, application control, SD-WAN, and Sophos Central cloud management, backed by up to 15.5 Gbps firewall throughput. Nine 2.5 GE copper ports and an SFP fiber port give it a stronger wired interface mix than the Meraki MX75-HW, whose listed LAN bandwidth is 1 Gbps. The package includes one year of Standard Protection; unlike the XGS 118 Xstream options, this listing does not describe sandboxing or the same expanded Xstream feature set. It is a wired appliance, so businesses seeking a single device for both firewalling and Wi-Fi should look elsewhere.
Pros:- Lists up to 15.5 Gbps firewall throughput.
- Nine 2.5 GE copper ports and one SFP fiber port support wired network flexibility.
- Includes firewall, VPN, intrusion prevention, web security, and application control.
- Sophos Central cloud management and SD-WAN support multi-site administration and connectivity.
Cons:- Included Standard Protection is specified for one year.
- The listing does not describe the broader Xstream features included with the other XGS 118 bundles.
- Wired connectivity only; no wireless networking is specified.
Best for: Mid-sized businesses that need cloud-managed firewall, VPN, SD-WAN, and application controls on a multi-gigabit wired network.
Not ideal for: Organizations that want the broader Xstream Protection features, built-in wireless, or a longer included protection term.
- Model:XGS 118 Gen 2
- Firewall throughput:Up to 15.5 Gbps
- Ports:9 x 2.5 GE copper and 1 x SFP fiber
- LAN port bandwidth:2500 Mbps
- Included protection:1-year Standard Protection
- Features:Firewall, VPN, intrusion prevention, web security, application control, and SD-WAN
- Management:Sophos Central cloud-based management
- Operating system:Sophos OS
Our verdict“Choose the Standard Protection XGS 118 when core business security and multi-gigabit ports matter more than the Xstream bundles’ expanded protections.”
SonicWall TZ570 Gen7 Firewall Appliance
The SonicWall TZ570 Gen7 is a strong fit for small and midsize businesses that need VLAN segmentation, VPN, secure SD-WAN, and centralized administration without relying on built-in wireless. It lists up to 4 Gbps firewall throughput and support for up to 1.25 million concurrent connections, positioning it between the Meraki MX75-HW’s 1 Gbps firewall figure and the Sophos XGS 118 Gen2’s 15.5 Gbps. Its threat-protection features include RTDMI, DPI-SSL, IPS, and Capture ATP, while NSM provides centralized management. The main caveat is that this listing is appliance only: no service subscription is included, so the stated threat features may require separate service coverage. Compared with the Meraki, the TZ570 emphasizes segmentation and SonicWall management rather than the same stated zero-touch cloud provisioning approach.
Pros:- Lists up to 4 Gbps firewall throughput and up to 1.25 million concurrent connections.
- Supports VLAN segmentation, secure SD-WAN, and VPN.
- Threat feature set lists RTDMI, DPI-SSL, IPS, and Capture ATP.
- NSM provides centralized management.
Cons:- No service subscription is included with the appliance.
- Wired Ethernet connectivity only; wireless networking is not provided.
- Its 4 Gbps stated firewall throughput is below the Sophos XGS 118 Gen2’s listed 15.5 Gbps.
Best for: Branch and midsize business administrators who need VLAN segmentation, secure SD-WAN, VPN, and centralized SonicWall management.
Not ideal for: Buyers who want an included security service subscription or wireless connectivity in the same appliance.
- Model:TZ570
- Firewall throughput:Up to 4 Gbps
- Concurrent connections:Up to 1.25 million
- Number of ports:9
- Data transfer rate:2.5 Gbps
- Operating system:SonicOS 7.0
- Management:NSM centralized management
- Included service subscription:None
Our verdict“Pick the TZ570 when segmentation and SonicWall centralized management suit your branch design, and plan separately for security services.”
SonicWall TZ570W Wireless Gen7 Firewall
The TZ570W is the clearest fit here for a small or midsize business that wants firewall, VPN, and wireless in one appliance. Its built-in dual-band Wi-Fi 5 can reduce the need for a separate access point, while SD-WAN and remote-access VPN support help connect branches and mobile staff. SonicWall lists throughput up to 3.0 Gbps and capacity for up to 1.25 million concurrent connections, giving it more headroom than a basic branch gateway.
Compared with the TZ280W, this model offers a higher listed connection capacity, but the TZ280W has newer Wi-Fi 6. The main catch is that this is hardware only: threat protection services and support require a separate subscription. I’d choose it for integrated networking, not for buyers seeking a subscription-ready bundle.
Pros:- Built-in dual-band Wi-Fi can reduce the need for a separate access point.
- Supports SD-WAN and site-to-site and remote-access VPN.
- Includes security capabilities such as Capture ATP, RTDMI, and DPI-SSL.
- Supports up to 1.25 million concurrent connections.
Cons:- No service subscription is included, so security services and support require separate purchasing.
- Uses Wi-Fi 5 rather than the Wi-Fi 6 found on the SonicWall TZ280W.
Best for: Small and midsize businesses that want a single appliance for wired security, VPN, SD-WAN, and built-in office Wi-Fi.
Not ideal for: Buyers who need Wi-Fi 6 or want security services and support included with the appliance.
- Model:TZ570W
- Wireless:Dual-band 802.11ac Wave 2 (Wi-Fi 5)
- Throughput:3.0 Gbps
- Data transfer rate:4 Gbps
- Ports:10
- Concurrent connections:Up to 1.25 million
- Operating system:SonicOS 7.0
- Security features:Capture ATP, RTDMI, DPI-SSL
- Included subscription:None
Our verdict“Choose the TZ570W if you want built-in business Wi-Fi and substantial connection capacity, and are prepared to add a service subscription.”
Sophos XGS 118 Gen2 Network Security Appliance (Hardware Only)
For a site built around fast wired connections, the Sophos XGS 118 Gen2 stands apart with nine 2.5 GE copper ports and an SFP fiber port. That mix gives teams more options for connecting high-speed devices and fiber uplinks than the 1GbE ports listed for the SonicWall TZ280W. Sophos also lists firewall throughput up to 15.5 Gbps, while Sophos Central provides cloud-based management for distributed administration.
The tradeoff is the package: this is hardware only, and a Sophos subscription is required for IPS, web security, VPN, and advanced threat defense. That makes it less ready to deploy as a protected gateway than the Fortinet FortiGate-60F bundle, which includes a year of services and support. I’d shortlist the XGS 118 for port density and wired capacity, but budget for licensing before relying on its security services.
Pros:- Nine 2.5 GE copper ports support faster wired connections than standard 1GbE ports.
- Includes an SFP fiber port for fiber connectivity.
- Listed firewall throughput is up to 15.5 Gbps.
- Sophos Central supports cloud-based management.
Cons:- Appliance-only package does not include a Sophos subscription.
- IPS, web security, VPN, and advanced threat defense require a subscription.
- Wired-only connectivity means wireless access requires separate equipment.
Best for: IT teams at branch offices or small and midsize businesses that need multiple 2.5GbE connections, a fiber port, and cloud-managed administration.
Not ideal for: Buyers who want included threat protection, or sites that need built-in wireless rather than a wired-only appliance.
- Model:XGS 118 Gen2
- Copper ports:9 x 2.5 GE
- Fiber port:1 x SFP
- Firewall throughput:Up to 15.5 Gbps
- Maximum upstream data transfer rate:7,750 Mbps
- Operating system:Sophos Firewall OS
- Connectivity:Ethernet and optical fiber
- Management:Sophos Central cloud management
- Included hardware:Appliance only; subscription sold separately
Our verdict“Pick the XGS 118 Gen2 for a high-capacity, multi-gig wired site if you are ready to purchase the required Sophos subscription separately.”
Fortinet FortiGate-60F Network Security Appliance with 1-Year FortiGuard UTP and FortiCare Premium
The FortiGate-60F bundle is the easiest fit in this group for a business that wants protection and support included for its first year. It pairs the appliance with one year of FortiGuard UTP and FortiCare Premium, including web filtering and anti-botnet protection. That is a meaningful difference from the hardware-only SonicWall TZ570W and Sophos XGS 118 Gen2, where the buyer must arrange subscriptions separately.
This bundled approach makes deployment planning simpler, but the available throughput data is less compelling for buyers comparing high-capacity wired gateways: the listing gives a 1 Gbps data transfer rate, rather than the XGS 118’s stated 15.5 Gbps firewall throughput. The FortiGate-60F also targets medium-sized businesses, not larger enterprise networks. I’d favor it when included services matter more than maximum listed throughput.
Pros:- Includes one year of FortiGuard UTP and FortiCare Premium.
- Provides web filtering and anti-botnet protection.
- Offers Ethernet and Wi-Fi connectivity.
- Combines the appliance and an initial service term in one bundle.
Cons:- Listed data transfer rate is 1 Gbps, below the stated firewall throughput of the Sophos XGS 118 Gen2.
- The included service term is limited to one year.
- The stated target is medium-sized businesses rather than larger enterprise infrastructure.
Best for: Medium-sized businesses that want a firewall with a defined first-year term of threat protection and premium support included.
Not ideal for: Large enterprises or high-throughput sites that need more capacity than the listed 1 Gbps data transfer rate.
- Model:60F-1YR-UTP
- Operating system:FortiOS
- Ports:13
- Data transfer rate:1 Gbps
- RAM:2 GB
- Connectivity:Ethernet and Wi-Fi
- Wireless standard:802.11ac
- Included services:1 year of FortiGuard UTP and FortiCare Premium
Our verdict“Choose the FortiGate-60F bundle if you value included first-year protection and support more than the higher listed throughput of the Sophos XGS 118 Gen2.”
SonicWall TZ280W Next-Generation Firewall Appliance
The TZ280W suits small businesses and branch offices that want current wireless standards alongside firewall, VPN, and Secure SD-WAN functions. Its Wi-Fi 6 is a clear advantage over the Wi-Fi 5 radio in the SonicWall TZ570W, while the eight 1GbE ports and two 1G SFP ports give a branch more wired connection choices. Listed firewall inspection throughput reaches 2.5 Gbps, with threat prevention throughput up to 1 Gbps.
The catch is the subscription model: this listing is hardware only, and security services, firmware updates, and support must be purchased separately. That contrasts with the FortiGate-60F bundle, which includes a year of protection and support. I’d choose the TZ280W for Wi-Fi 6 and branch connectivity, but not if you need a ready-to-run service package or high-speed multi-gig ports.
Pros:- Built-in 802.11ax Wi-Fi 6 is newer than the Wi-Fi 5 wireless on the SonicWall TZ570W.
- Provides up to 2.5 Gbps firewall inspection throughput.
- Includes eight 1GbE Ethernet ports and two 1G SFP ports.
- Supports VPN and Secure SD-WAN for branch connectivity.
Cons:- Security services, firmware updates, and support require a separate subscription.
- Threat prevention throughput is listed at up to 1 Gbps.
- The Ethernet ports are 1GbE rather than the 2.5 GE ports on the Sophos XGS 118 Gen2.
Best for: Small businesses and branch offices that want Wi-Fi 6, VPN, and Secure SD-WAN in a desktop appliance.
Not ideal for: Organizations that need included subscriptions and support, or wired ports faster than 1GbE.
- Model:TZ280W
- Firewall inspection throughput:Up to 2.5 Gbps
- Threat prevention throughput:Up to 1 Gbps
- IPSec VPN throughput:Up to 1.2 Gbps
- Ethernet ports:8 x 1GbE
- SFP ports:2 x 1G SFP
- Wireless:802.11ax (Wi-Fi 6)
- Dimensions:14.4 x 8.7 x 2.7 inches
- Included:Hardware only; service subscription not included
Our verdict“Choose the TZ280W for a compact branch network that needs Wi-Fi 6 and SD-WAN, provided you plan separately for its subscription services.”
MX105-HW Cloud-Managed Security Appliance
The MX105-HW is the rack-oriented choice for teams that want to manage network security remotely through the cloud. Its 1U form factor, 10 Gigabit Ethernet ports, and listed throughput up to 3 Gbps make it more suited to a central wiring closet or managed branch than the desktop-focused SonicWall TZ280W. Layer 7 visibility can help administrators identify application traffic, while VPN and SD-WAN support cover common site-to-site needs.
Compared with the Sophos XGS 118 Gen2, the MX105-HW emphasizes cloud-based remote management and rack installation rather than multiple 2.5 GE copper ports and an SFP fiber port. Its main drawback is licensing: a license is not included, so the appliance alone does not cover the full service commitment. The listed operating system is Cisco IOS, a detail buyers should verify against their intended management and licensing setup before choosing it.
Pros:- Cloud-based remote management suits distributed network teams.
- Includes 10 Gigabit Ethernet ports.
- Supports up to 3 Gbps throughput, VPN, and SD-WAN.
- Layer 7 visibility helps administrators inspect application-level traffic.
Cons:- License is not included.
- The 1U rack-mountable format is less suitable for sites without rack space.
- Unlike the SonicWall TZ280W, no built-in wireless is listed.
Best for: IT teams managing rack-mounted branch or central-site networks that want cloud-based administration, 10 Gigabit Ethernet ports, and SD-WAN.
Not ideal for: Buyers who need included licensing or a desktop appliance with built-in Wi-Fi.
- Throughput:Up to 3 Gbps
- Ethernet ports:10 Gigabit Ethernet ports
- Management:Cloud-managed
- Features:Next-generation firewall, VPN, SD-WAN, Layer 7 visibility
- Form factor:1U rack-mountable
- Cooling:Dual fans
- Operating system:Cisco IOS
- Security protocols:SSL/TLS, IPsec VPN, Auto VPN
- Warranty:Limited lifetime
Our verdict“Choose the MX105-HW for a rack-based network where cloud management and 10 Gigabit Ethernet matter, after confirming licensing requirements.”
SonicWall TZ270 Gen 7 Firewall with 3-Year APSS and 1-Year Cloud Secure Edge
I’d choose the TZ270 Gen 7 when a small business wants a cloud-connected firewall with security services already bundled, rather than a hardware-only starting point. Its three-year APSS subscription covers gateway antivirus, intrusion prevention, application control, content filtering, and Capture ATP sandboxing; TLS 1.3 inspection adds visibility into encrypted traffic. Zero-Touch deployment and centralized management also suit branch rollouts where an onsite IT specialist may not be available. Compared with the SonicWall TZ80, this is the more ready-to-deploy choice because the TZ80 is a secondary appliance without included security services. The tradeoff is that the TZ270’s listing gives conflicting port counts, and the included Cloud Secure Edge coverage is limited to one year. I’d verify the exact interface configuration before ordering.
Pros:- Three-year APSS bundle includes multiple threat-protection services and Capture ATP.
- TLS 1.3 decryption helps inspect encrypted traffic for threats.
- Zero-Touch deployment and centralized management support remote branch setup.
- Secure SD-WAN and site-to-site VPN connect branch networks.
Cons:- The listed port count of four conflicts with the description of eight Gigabit Ethernet interfaces.
- Cloud Secure Edge coverage lasts one year, shorter than the APSS term.
- The stated 2 Gbps transfer rate does not clarify performance under every security workload.
Best for: Small-business IT teams and retailers setting up a new branch who want bundled security services, VPN connectivity, and remote deployment support.
Not ideal for: Buyers who need a clearly verified port layout or a longer included cloud-edge term; the listed port count conflicts with the eight-interface description, and Cloud Secure Edge is included for one year.
- Model:TZ270 Gen 7
- Operating system:SonicOS 7
- Security subscription:3-year Advanced Protection Service Suite (APSS)
- Cloud Secure Edge:1 year
- Ethernet interfaces:Eight Gigabit Ethernet interfaces described; listing also states 4 ports
- Data transfer rate:2,000 Mbps
- Concurrent connections:Up to 750,000
- Security features:Gateway AV, intrusion prevention, application control, content filtering, Capture ATP, RTDMI, and RFDPI
- Connectivity features:Secure SD-WAN, site-to-site VPN, TLS 1.3 decryption, and Zero-Touch deployment
Our verdict“Choose the TZ270 if you want a small-branch firewall with a substantial security subscription included, but confirm the port configuration first.”
SonicWall TZ80 High Availability Firewall Appliance
The TZ80 has a narrow but useful role: it is a compact secondary appliance for a SonicWall high-availability setup, not a stand-alone firewall purchase. In an active/standby pair, it can take over if the primary unit fails, helping a small office or branch limit disruption. Its stated 750 Mbps threat-prevention and IPsec VPN throughput makes its capacity easier to compare with the TZ270’s 2 Gbps listed transfer rate, but those figures describe different models and workloads. Unlike the TZ270, the TZ80 includes no security services or support, so subscription costs and a compatible primary must be part of the plan. That makes it a poor first appliance for a new network. I’d pick it only when failover is the goal and the matching system is already in place.
Pros:- Supports stateful active/standby failover.
- Up to 750 Mbps stated firewall, threat-prevention, and IPsec VPN throughput.
- Compact desktop form suits branch or SOHO installations.
- Includes four Gigabit Ethernet ports and one SFP port.
Cons:- Requires a matching primary firewall, limiting its use as a stand-alone appliance.
- Security services and support are not included.
- The product data does not specify the subscription needed for the listed remote-access and security features.
Best for: Organizations with a compatible SonicWall primary firewall that need a dedicated desktop secondary for active/standby failover.
Not ideal for: Small offices buying their first firewall, or teams expecting included threat-protection services and support; this unit requires a matching primary and separate active services.
- Model:TZ80
- Part number:03-SSC-2749
- Operating system:SonicOS 8
- Form factor:Compact desktop
- Ports:4 x 1GbE, 1 x SFP
- Firewall throughput:Up to 750 Mbps
- Threat prevention throughput:Up to 750 Mbps
- IPsec VPN throughput:Up to 750 Mbps
- Intended use:High-availability secondary appliance
Our verdict“Buy the TZ80 as a failover partner for a compatible SonicWall primary, not as your first or only firewall.”
SonicWall TZ670 Gen7 Firewall – Multi‑Gig Throughput Wi‑Fi Security Appliance
For a distributed business whose firewall must keep pace with fast uplinks, I’d rank the TZ670 ahead of the compact TZ270: it lists 5 Gbps firewall throughput, 2.5 Gbps threat-prevention performance, and 10 GbE interfaces. That headroom can reduce the chance that security inspection becomes the bottleneck as branch traffic grows. Its 1.5 million concurrent-connection capacity and Capture ATP sandboxing also suit busier environments handling many sessions and unknown files. Dual-band 802.11ac Wi-Fi adds wireless capability in the appliance, while NSM supports centralized oversight across sites. The tradeoff is that this listing is appliance-only, unlike the TZ270 bundle with three years of APSS. Buyers must account for separate security services, and the product data does not detail a bundled cloud-management or security-service term.
Pros:- Up to 5 Gbps firewall throughput and 2.5 Gbps threat-prevention performance.
- Ten 10 GbE interfaces support high-capacity network links.
- Capture ATP sandboxing and other listed security engines help inspect suspicious files and traffic.
- Centralized NSM management supports multi-site administration.
Cons:- Appliance-only listing requires a separate security-services purchase.
- The product data does not specify an included subscription term.
- Its performance and interface capacity may exceed the needs of smaller offices.
Best for: IT teams in midsize or distributed organizations that need multi-gig firewall capacity, 10 GbE connectivity, and centralized oversight across locations.
Not ideal for: Small offices seeking an all-in-one purchase with security services included, or buyers who do not need the TZ670’s throughput and interface capacity.
- Firewall throughput:5 Gbps
- Threat-prevention throughput:2.5 Gbps
- Concurrent connections:1.5 million
- Number of ports:10
- Interface speed:10 GbE
- Wireless:Dual-band 802.11ac
- Security protocols and services:WPA3, RTDMI, IPS, anti-malware, and Capture ATP
- Management:Centralized management via NSM
Our verdict“Choose the TZ670 when multi-gig throughput and 10 GbE matter more than receiving a security subscription in the box.”
Firewalla Purple SE Cyber Security Firewall for Home & Business – Malware Protection, Parental Controls, VPN Server, No Monthly Fee
The Firewalla Purple SE is the approachable choice here for a home, small office, or IoT-heavy network where app-based controls matter more than enterprise throughput. Its cloud-based behavior analytics, IDS/IPS, and smartphone-managed parental controls make it easier to oversee connected devices without adopting the centralized enterprise systems used by the Meraki MX95. It can work as a router or in transparent bridge mode, so buyers have some flexibility when replacing or supplementing existing equipment. The built-in OpenVPN server is another useful feature for remote access. Capacity is the main compromise: 500 Mbps IPS throughput and a 100 Mbps LAN port are limiting for faster connections and heavier traffic. Simple Mode may also require router-specific configuration, so I’d check compatibility before choosing it.
Pros:- IDS/IPS and cloud-based behavior analytics cover wired and wireless devices.
- Smartphone app supports parental controls and device management.
- Built-in OpenVPN server is listed without a monthly subscription fee.
- Can operate as a primary router or in transparent bridge mode.
Cons:- 500 Mbps IPS throughput may constrain faster internet connections.
- The listed LAN port speed is 100 Mbps, limiting wired-device throughput.
- Simple Mode compatibility can depend on the existing router and may need extra setup.
Best for: Households, home offices, and small teams that want app-managed device controls, parental settings, and basic network threat monitoring.
Not ideal for: Users with internet service above the appliance’s 500 Mbps IPS ceiling, buyers needing faster wired LAN connectivity, or organizations requiring enterprise branch management.
- Model:Purple SE
- IPS throughput:500 Mbps
- LAN port speed:100 Mbps
- Ports:1 LAN port
- Wi-Fi:Dual-band Wi-Fi 5 (802.11ac)
- RAM:3 GB
- Operating system:Linux
- Control method:App
- Security protocol:WPA2-PSK
Our verdict“Pick the Purple SE for app-led security and family controls on a modest-speed network, not for high-throughput business use.”
Meraki MX95-HW Security Appliance Bundle
The Meraki MX95-HW is the clearest fit for a medium-sized branch that values centralized cloud administration over a compact, low-complexity setup. The Meraki Dashboard supports configuration and remote troubleshooting across sites, while SD-WAN and Layer 7 visibility help teams manage application traffic centrally. Its 2 Gbps throughput and stated capacity of up to 500 users place it above the home-focused Firewalla Purple SE, but below the TZ670’s listed 5 Gbps firewall capacity. Dual 2.5GbE WAN ports and dual 10GbE SFP+ ports provide useful options for WAN and high-speed network links. The key caveat is licensing: the listing says no license is included, so buyers need to confirm the required service and feature entitlements. This rack-mountable appliance is more than most small offices need.
Pros:- Meraki Dashboard supports centralized configuration and remote troubleshooting.
- 2 Gbps throughput and stated capacity for up to 500 users suit medium-sized branches.
- SD-WAN and Layer 7 application visibility support traffic management.
- Dual 2.5GbE WAN and dual 10GbE SFP+ ports offer flexible connectivity.
Cons:- No license is included, so buyers must obtain the licensing needed for full functionality.
- The 1U rack-mountable design and enterprise feature set may be excessive for small networks.
- The product data does not specify the duration or scope of any cloud-management entitlement.
Best for: IT teams managing medium-sized branches that need cloud-based configuration, remote troubleshooting, SD-WAN, and high-speed uplink options.
Not ideal for: Home users and small offices seeking a simple, self-contained appliance, or buyers who need licensing included with the hardware.
- Model:MX95-HW
- Throughput:2 Gbps
- User capacity:Up to 500 users
- WAN ports:Dual 2.5GbE RJ45
- SFP+ ports:Dual 10GbE
- Form factor:1U rack-mountable
- Management:Meraki Dashboard cloud management
- Operating system:Meraki OS
- License:Not included
Our verdict“Choose the MX95-HW for centrally managed branch networks when you can plan for licensing separately.”

How We Picked
I ranked these appliances by how well they answer the actual needs behind a cloud-managed firewall purchase: remote administration, security-service coverage, network fit, deployment flexibility, and room to grow. I also weighed whether the listing includes hardware alone or a defined protection plan, and whether wireless or SD-WAN is built into the offering. Those differences affect ongoing administration and what a buyer must arrange separately.
The ranking favors options with a clear use case and a useful balance of management, protection, and flexibility. That puts the Meraki MX75-HW first for a broad cloud-managed deployment, while Sophos and Fortinet options stand out for their service-plan choices and security focus. I distinguish near-identical hardware bundles by their included coverage rather than treating them as separate platform designs. More specialized or home-oriented options rank lower for general business use, not because they lack value, but because their fit is narrower.
Factors to Consider When Choosing Cloud Based Firewall Appliances
Choosing a cloud-managed appliance is a decision about the full operating model, not just the firewall chassis. I would compare how the platform is managed, what protection is included, and who will maintain the network after installation.
Separate cloud management from cloud security
A cloud dashboard and cloud-delivered threat services are related but distinct capabilities. Management may let an administrator configure policies remotely, while security subscriptions can add threat intelligence, intrusion prevention, or web controls. A common mistake is assuming a cloud-managed label means every protection feature is included. Check which functions remain active with the hardware alone and what requires an ongoing plan. If your team already operates a separate security stack, paying for overlapping services may add complexity without much benefit. If you lack dedicated staff, bundled protection can make responsibilities clearer.
Size for inspected traffic, not the headline throughput
Firewall capacity can change sharply when inspection features are enabled, so raw throughput figures may not represent everyday performance. Estimate the traffic that will pass through the appliance with the policies your team actually plans to use. Include VPN users, cloud applications, busy periods, and expected growth rather than sizing only for today’s internet connection. An undersized unit can become a bottleneck when security inspection is active. An oversized unit adds expense and may leave capacity unused. Ask vendors which performance figures apply to the feature combination you intend to run.
Treat subscriptions as part of the appliance decision
Bundle terms affect both capability and future flexibility. A longer protection term can reduce renewal work, but it also commits the organization to a specific service plan and vendor before needs may be fully known. Hardware-only listings can suit teams with an existing licensing arrangement, yet they may leave a new buyer without the protection they expected. Compare included services, term length, renewal process, and what happens when a subscription ends. Avoid comparing two listings by chassis name alone; the bundle can be the larger practical difference. Keep a record of renewal dates and the features tied to each plan.
Decide whether wireless belongs in the firewall
Built-in wireless can simplify a small site with limited equipment, but it is not automatically the best network design. Separate access points may provide easier placement, broader coverage, and a clearer upgrade path. A wireless firewall can be convenient for a branch or compact office where fewer devices are easier to manage. Think about the number of users, physical layout, guest access, and whether wireless faults should affect firewall maintenance. Do not treat the presence of Wi-Fi as proof that coverage will suit every building. Confirm the wireless capabilities and management model against your site plan.
Check management fit and recovery procedures
Cloud administration can make multi-site policy changes easier, but it also means the team must understand account access, roles, and recovery options. Before buying, confirm who can administer the tenant and how access is restored if the primary administrator leaves. Review whether policy changes can be staged, audited, and rolled back, especially for remote sites where a configuration error can interrupt connectivity. Small teams may value a simpler interface more than deep customization. Larger IT teams may need granular controls and integration with existing monitoring workflows. A good fit is the platform your staff can operate consistently, not simply the one with the longest feature list.
Plan for redundancy and future network changes
A single firewall can be sufficient for a small office, but a business that cannot tolerate an outage should plan for redundancy before selecting hardware. Check whether the chosen model supports the failover arrangement you need and whether a second unit requires separate licensing or configuration work. Also account for future changes such as faster internet, new branches, additional VPN users, or network segmentation. Buying only for the current layout can force an early replacement when a new requirement appears. At the same time, avoid paying for high-end capacity based on hypothetical growth with no timeline. A practical forecast helps balance resilience and headroom.
Frequently Asked Questions
Does a cloud-managed firewall keep working if the cloud dashboard is unavailable?
That depends on the appliance and the service design, so I would verify behavior with the manufacturer before purchase. Many cloud-managed firewalls apply their current local configuration even when the management service cannot be reached, but remote changes and some cloud-connected features may be unavailable during an outage. Ask whether traffic inspection, VPN access, and policy enforcement continue independently. Also check how the device reports the outage and how configuration changes are synchronized afterward. This matters most for remote sites with limited hands-on support.
Should I choose a hardware-only firewall or a bundle with protection services?
Hardware-only can make sense when your organization already has a licensing plan or a security team that knows which services it needs. For a new deployment, a bundle can reduce guesswork by including a defined set of protections for a stated term. Compare the exact services rather than relying on labels such as standard or advanced, since coverage differs by vendor. Also confirm what remains available after the term ends and how renewals are handled. The Sophos XGS 118 listings in this roundup show why the package can matter as much as the appliance model.
Can a home-focused firewall work for a small business?
It can suit a very small office if its management, security, and network features match the actual workload. A home-oriented device may be easier to operate and may cover basics such as VPN access or family-style controls, but business needs can include multiple sites, staff roles, audit records, and predictable support. Check the number of users and devices it can handle, how policies are managed, and what happens when the business grows. Firewalla Purple SE is positioned for home and small-business use, unlike the more conventional business appliances here. A small business with compliance or uptime needs should verify those requirements before choosing a compact option.
When is built-in Wi-Fi worth choosing over a separate access point?
Built-in Wi-Fi is appealing when a small site needs a compact setup and has a simple coverage area. A separate access point can be a better fit when you need to place wireless equipment centrally, expand coverage, or replace it without changing the firewall. Consider whether guest access and wireless troubleshooting should be managed alongside firewall policies. Also check how many clients and what coverage the wireless model is designed to support. The SonicWall TZ570W and TZ280W offer wireless options, while a wired firewall can leave that choice open.
How should I choose between Meraki MX75, MX95, and MX105 models?
Start with expected traffic, site count, security features, and the growth you can reasonably forecast, then compare the specifications and service terms for each model. The MX75-HW is the roundup’s broad-use cloud-managed pick, while the MX95 and MX105 listings suggest options for buyers comparing higher-tier appliance choices. Do not assume the model number alone tells you what capacity you need; inspect performance with the features your network will use. Check licensing and bundle details as well, since those affect management and protection over time. If your requirements are modest, paying for unused headroom may not improve day-to-day administration.
Conclusion
For most organizations seeking a cloud-managed business firewall, I recommend the Meraki MX75-HW as the best overall because its cloud-first management and SD-WAN make a strong general-purpose combination. For best value through bundle choice, compare the Sophos XGS 118 versions and select the protection term that matches your needs rather than defaulting to hardware-only. The best premium direction is a higher-capacity option such as the Meraki MX105 or SonicWall TZ670 when traffic and growth justify the extra headroom. For beginners, a clearly bundled Sophos or Meraki setup can simplify the initial decision; confirm what services are included before ordering. For wireless-focused sites, look at the SonicWall TZ570W or TZ280W, while Firewalla Purple SE is the more specialized choice for home and very small-business networks. Match the appliance to the people who will manage it, the protection you need, and the capacity your network can support.