TL;DR
Recent observations suggest that malicious software developers are using Google Ads to promote their products. While the details are still emerging, this raises questions about platform enforcement and security risks for users.
Security analysts have detected that malicious software developers are using Google Ads to promote their products, despite platform policies against such advertising. This development raises concerns about the effectiveness of advertising enforcement and the potential reach of malicious campaigns.

Get business pricing on networking and server gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Multiple cybersecurity firms and researchers have reported observing suspicious ad campaigns on Google Ads that appear to promote malicious software, including ransomware, remote access tools, and fake security applications. These ads often mimic legitimate services, targeting a broad audience through targeted keywords and geo-specific campaigns.
According to sources familiar with the investigations, these ads are crafted to evade detection by using obfuscated URLs, misleading ad copy, and occasionally leveraging compromised accounts to run campaigns. While Google’s advertising policies explicitly prohibit the promotion of malware and malicious activities, enforcement appears inconsistent, with some campaigns remaining active for days or weeks.
Google has publicly stated that it employs automated systems and manual reviews to detect and remove malicious ads, but the recent activity suggests that bad actors are finding ways to circumvent these measures. The campaigns are often launched through the use of stolen payment methods or fake accounts, complicating detection efforts.
Implications for Platform Security and User Safety
This trend highlights significant challenges in online advertising moderation and the potential for malicious actors to exploit mainstream platforms for widespread distribution of harmful software. If such campaigns are not swiftly detected and removed, they can lead to increased malware infections, data breaches, and financial losses for unsuspecting users.
The incident underscores the importance of continuous monitoring and improved detection capabilities by advertising platforms like Google. It also raises questions about the adequacy of current policies and enforcement mechanisms to prevent the promotion of malicious content.
Products Worth Considering

Amazon Kindle Scribe (16GB) with Premium Pen, Tungsten
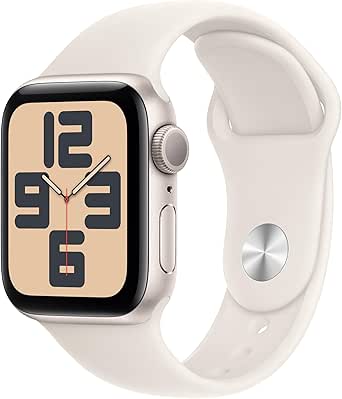
Apple Watch SE (2nd Generation) GPS 40mm Smartwatch with Starlight Aluminum Case and Starlight Sport Band (S/M)

Apple AirPods Pro 3 Wireless Earbuds with Active Noise Cancellation
As an affiliate, we earn on qualifying purchases.
Rise of Malicious Advertising in Search Ecosystems
Over recent years, cybercriminals have increasingly exploited online advertising networks to distribute malware, often by masquerading as legitimate services or using compromised accounts. Google Ads, being one of the largest advertising platforms globally, has been a target for these tactics, although the company maintains that it actively combats such misuse.
Past incidents have shown that malicious actors frequently adapt their methods to evade detection, including using ad copy that mimics trusted brands or leveraging new, disposable accounts. The current spike in activity appears to be part of this ongoing trend, with recent campaigns gaining visibility across various regions and languages.
Google has faced criticism in the past for delays in removing malicious ads, and the current developments suggest that the problem persists despite ongoing efforts.
Extent and Detection of Malicious Campaigns
It is not yet clear how widespread these malicious advertising campaigns are or how effectively Google’s current detection systems are responding. The activity appears to be ongoing, but detailed metrics and internal enforcement actions have not been publicly disclosed.
Experts suggest that malicious actors may be using increasingly sophisticated techniques to evade detection, but the full scope of the problem remains uncertain.
Monitoring and Policy Improvements Expected
Security researchers and industry analysts expect ongoing monitoring of ad campaigns and increased scrutiny by Google. The company may update its policies or improve automation tools to better detect and remove malicious ads.
Further investigations are likely to reveal more about the techniques used by malicious actors and the effectiveness of current enforcement measures. Users are advised to remain cautious when clicking on ads and report suspicious activity.
Key Questions
How are malicious ads on Google Ads detected?
Google uses automated detection systems combined with manual reviews to identify and remove malicious ads. However, malicious actors often use obfuscation techniques to evade detection, making enforcement challenging.
What types of malicious software are being promoted?
Reports indicate that ransomware, remote access tools, fake security applications, and other malware are being advertised through these campaigns.
Can users protect themselves from clicking malicious ads?
Yes, users should remain cautious with ads that seem suspicious or too good to be true, avoid clicking on unfamiliar links, and report suspicious ads to Google.
Will Google improve its detection of malicious ads?
Google has stated it is continuously working to enhance detection and enforcement, but the evolving tactics of malicious actors mean ongoing vigilance is necessary.
What should advertisers do to avoid being mistaken for malicious campaigns?
Advertisers should adhere strictly to Google’s advertising policies, use legitimate payment methods, and avoid misleading or deceptive content.
Source: hn